Nearly two million Quest Apartment Hotels customers affected by data breach
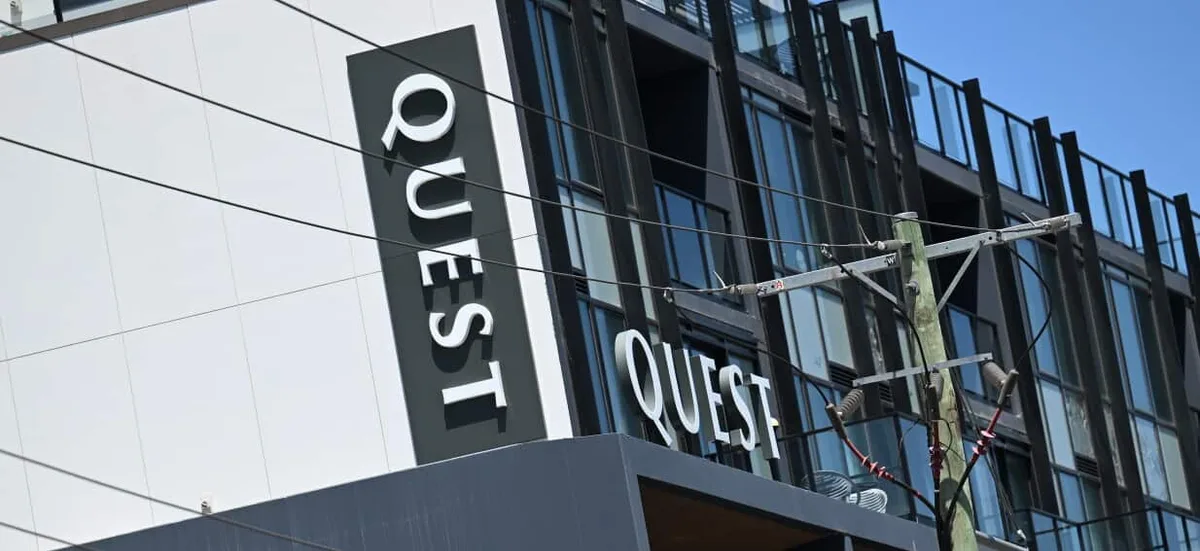
Personal information of nearly two million Quest Apartment Hotels customers has been compromised in a data breach, including credit card, passport and Medicare numbers.
Last month, the accommodation provider identified a cyberattack on a database system via a vulnerability in a third-party technology provider.
David Mansfield, the managing director of The Ascott Limited, which owns Quest Apartment Hotels, provided an update this week, saying a forensic data analysis revealed information relating to approximately 1,991,613 customers was affected.
The majority of information related to names and contacts, but also included:
Your trusted source for staying up-to-date with the world around you. Get free daily news updates and analysis, straight to your inbox.
Mansfield said the company was contacting those affected directly to inform them of which category they were in, the steps they could take, and available support.
"I recognise the concern this incident has caused. On behalf of Quest, I sincerely apologise to those who have been affected," he said.
Quest said it first identified an outage on its website on 17 August, with investigation revealing "a malicious attack" had exploited a vulnerability in a third-party service provider's software.
The company is advising customers to remain alert for suspicious emails, text messages and telephone calls, particularly communications requesting personal, financial or account information.
Quest said it was cooperating with the Office of the Australian Information Commissioner, the Australian Signals Directorate, the Australian Cyber Security Centre and Victoria Police.
Last year's Annual Cyber Threat Report warned cyberattacks were a growing problem in Australia, with financial losses, ransomware attack frequency, and the number of reported data breaches all increasing.
After a major data breach involving millions of Optus customers in 2022 , the federal government overhauled privacy laws, requiring companies to destroy or actively de-identify personal information as soon as it was no longer needed.
Paul Watters, chief executive of Cyberstronomy, which provides cyber risk expertise, said all businesses needed to have a clear understanding of the personal data they hold and why.
"Quest says all of the affected information came from records dating from before June 2025. That immediately raises a governance question: for each category of information, why was it still being retained?"
5News aggregated this summary from the outlet’s public feed. The full article, with all the context, is on www.sbs.com.au — the content belongs to SBS News - Latest.